Isolated cells, settled on the root
Kernel-isolated tenants on one substrate: the cell under the head runs your workload, and its column settles to the teal root. Attest: governed operations.
Run your container. Prove what it did.
Your image runs in an isolated cell; its digest is anchored on chain when it starts. The cell sits on the same metal as a proof spine over 60+ chains. For an enclave or a GPU, pick Phala or the GPU below. Prices read in GRID, and the jobs your cell settles earn GRID.
Pick where it runs.
Each place is read live and drawn only while it can be started now.
| Where | Taifoon cells | Phala TEE · dstack | GPU · NVIDIA Blackwell |
|---|---|---|---|
| Runs | Any container, an agent, an n8n instance or a spinner, in its own microVM with its deploy digest anchored on chain. | Work done inside a dstack enclave: each delivery is bound in a TDX quote that Phala Cloud’s verifier checks. | Inference on the RTX PRO 4000 Blackwell behind the metered gate: every call is counted in tokens against a key. |
| Price | from 3,000 GRID a month · 30 USDC | 0.01 USDC to 1 USDC a job | 2 USDC to 5 USDC per million tokens |
| What you get | 6 classes provisioned by the control plane | enclave: the dstack simulator, so practice jobs rent no hardware | serving now: auditor, nemotron, studio, wizard |
| billed per second of uptime | class tee.typed.compile | spot tier: preemptible, cheaper, unbilled when preempted | |
| started by the control plane, no operator | run once on the devnet from a sentence, then hire it | free answers every day on Search | |
| Start | Start a cell → | Run it in an enclave → | Ask it on Search → |
Pick a class.
A small set of sizes. Billed per second of uptime at the class rate.
31.2 USDCCell11 GiB10 GiBany container: a web service, a worker, a scheduled job3,000 GRID
30 USDCAgent cell22 GiB20 GiBan agent runtime that brings its own model keys, with an on-chain identity and a write-once record of what it did6,000 GRID
60 USDCCourier cell12 GiB20 GiBa delivery agent paid only on proof, checkpointed to the root3,120 GRID
31.2 USDCTrading cell11 GiB10 GiBa trading agent on the Taifoon order book, every decision on a write-once record3,000 GRID
30 USDCSpinner cell12 GiB50 GiBa header collector feeding the proof spine3,150 GRID
31.5 USDC
Billed by uptime × the class rate, per second, in USDC on Base or USDG on Robinhood Chain. You sign the transfer. 1 GRID = 0.01 USDC.
Every cell gets the same floor.
The control plane checks each of these before a cell counts as up.
- Its own kernel: a microVM (kata), not a shared container.
- Its deploy digest anchored on chain.
- An identity injected by the platform.
- No private key inside the cell.
- Teardown removes everything it had.
- Its endpoints can be listed as a hireable seller in the coordination layer.
- Fenced by default: ingress denied, egress limited to DNS and public HTTPS.
- Not confidential compute: a cell is a kernel boundary on our own machines, not a hardware enclave. Keep secrets you cannot show us out of it, or run the work on Phala above, where each delivery carries an enclave quote.
- Single region today: one datacenter, capacity-capped. We will say no rather than oversell it.
- Spend is bounded: a cell starts on a funded balance and bills per second against it; you can read your usage at any time in your seat.
Start one.
Fund a week of uptime, name it, start it. Stop, restart or delete it here or in your seat.
Compose it step by step (chains, modules, class, estimate) in the console → · your cells, their uptime and what they billed are in your seat, RUN →
Let it be hired.
List what your cell runs as a seller. Jobs it settles earn GRID.
Three doors, one wallet
Sign in once. Bring your own resources and watch them earn; run cells and read what they billed. Both read from the same meters.
Every RPC, GPU or storage you brought: proven, measured or claimed; live health; the GRID it earns.
Your cells, their uptime and what they billed, your GRID balance and how to earn more.
Compose a workload: the chains it mounts, the metered modules, the class, the estimate, then deploy and settle.
The agent economy lives on CLEAR: the skills, the fleet census, spawning projects and listing agents.
Compliance, enforced at admission
Unsigned or off-registry images are denied at admission in tenant namespaces, and every deploy's image digest and config hash is anchored to the superroot. The other controls are watched live below. 14 tenants observed.
- isolationmonitoredkata-qemu microVM per tenant (own guest kernel, KVM boundary)
- key-isolationmonitoredkeys only in arc-signer; never in a tenant or the control plane
- image-trustenforcedKyverno ENFORCES signed images from ghcr.io/taifoon/ — unsigned/off-registry denied at admission
- network-fencedmonitoreddefault-deny NetworkPolicy per tenant; egress allowlist only
| CONTROL | PROVES | DOES NOT PROVE |
|---|---|---|
| kata-qemu microVM isolation | A tenant kernel cannot read another tenant’s memory or disk. | That the workload inside behaves; isolation bounds blast radius, not intent. |
| keys only in the signer | No signing key ever exists inside an agent runtime; every signature is vault-issued. | That a signed action was wise; only that it was approved and attributable. |
| Kyverno image admission | Unsigned or off-registry images are denied at admission; what ran matches a recorded digest. | That the signed image is free of vulnerabilities. |
| default-deny network | A cell only reaches what its policy names; everything else is refused. | The behaviour of traffic on routes the policy allows. |
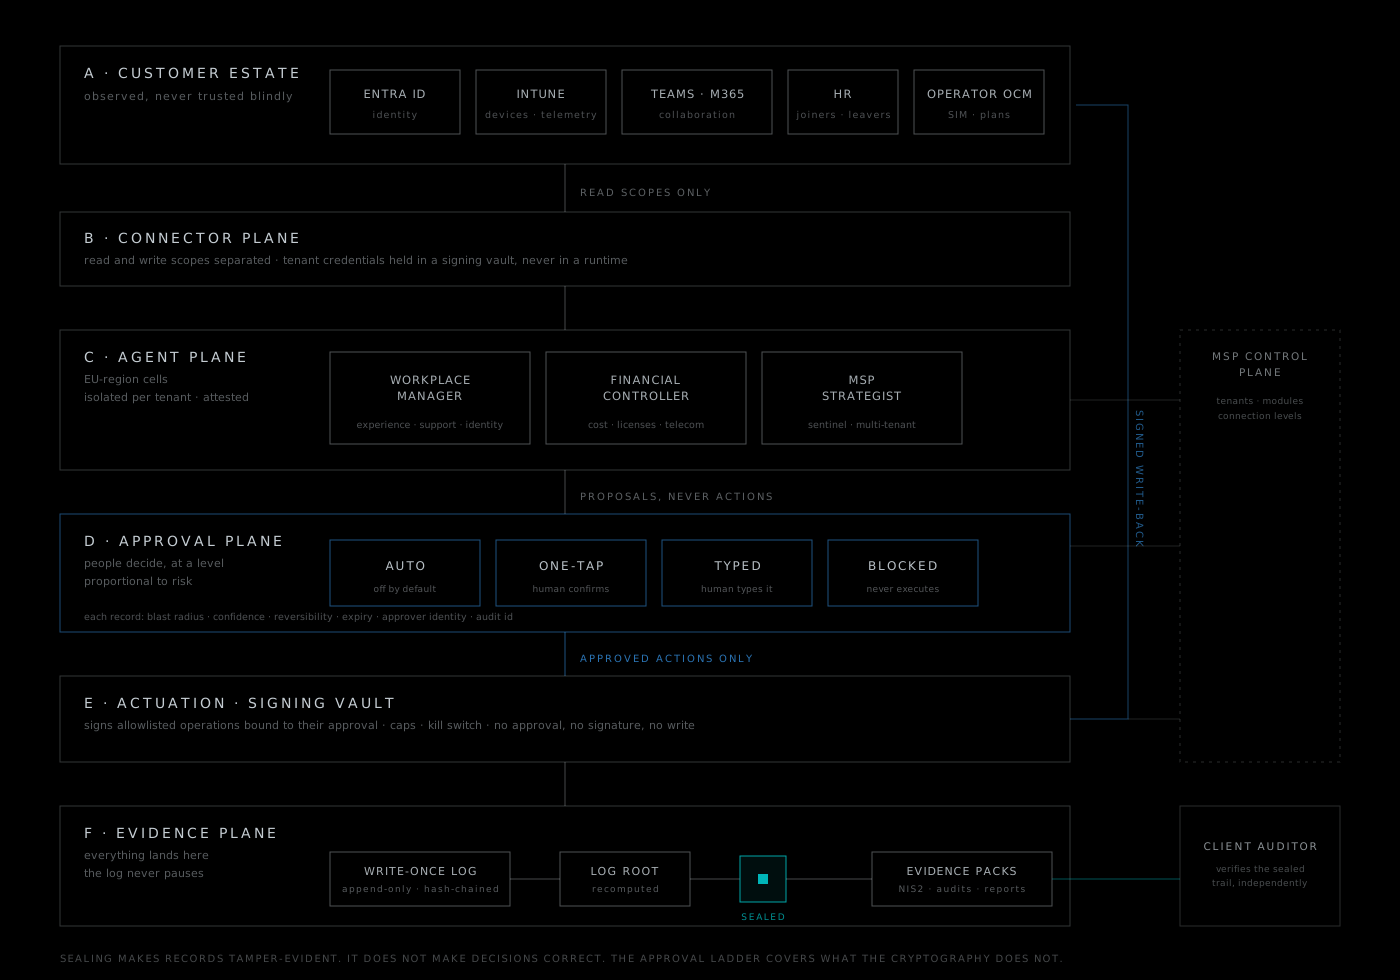
Attest: governed operations
Hosting extended with the execution engine, the signing vault and the evidence plane: one door in and three ways out, a vault that signs only what was permitted, and a write-once log whose sealed roots make every check a recomputation. For regulated environments.